A software bill of materials (SBOM) identifies components in a software artifact. It improves visibility, but it does not prove that dependencies are safe, builds are trustworthy, or vulnerabilities are fixed. Supply-chain security needs controls from source and dependency selection through build, release, deployment, and response.
Know What You Build and Buy
Inventory first-party repositories, open-source packages, base images, build tools, registries, hosted services, and commercial components. Assign owners and criticality.
Generate SBOMs automatically for released artifacts in a standard format such as SPDX or CycloneDX. Preserve the relationship between source, build, artifact digest, SBOM, and deployed version.
Protect Source Control
Require strong authentication, least privilege, protected branches, review for material changes, and controlled automation tokens. Restrict who can change workflows, branch rules, release configuration, and dependency sources.
Scan for secrets and respond by revoking them—not merely deleting the commit. Preserve audit events and review unusual repository access.
Control Dependencies
Pin or lock versions, use trusted registries, verify package identity and integrity, and review new dependencies for maintenance, licence, provenance, and risk. Reduce unnecessary packages.
Automated vulnerability alerts require triage based on exploitability and actual deployment context. A long scanner queue is not risk management.
Harden the Build
Isolate builds, minimise network access, use ephemeral workers, protect signing keys, and separate build administration from release approval. Produce immutable artifacts once, promote the same digest between environments, and avoid rebuilding production from an unverified state.
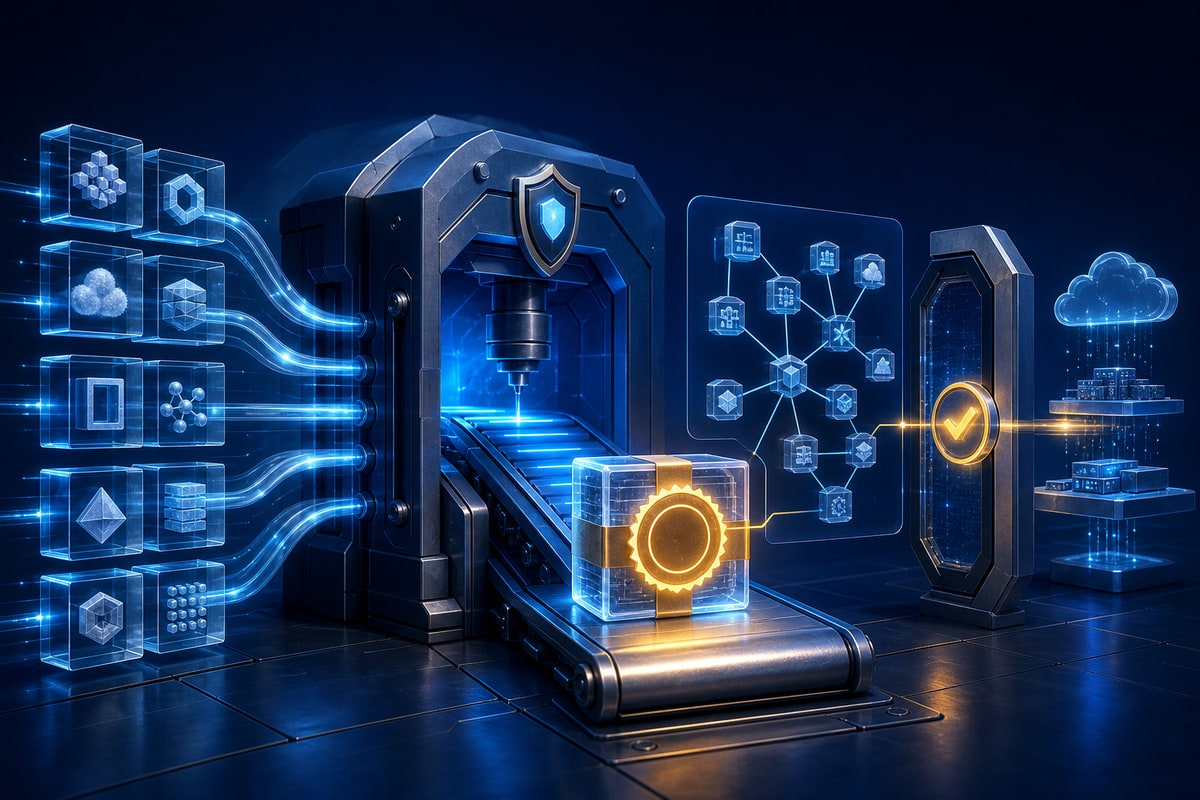
Record provenance that explains what source, builder, parameters, and dependencies created an artifact. Sign artifacts or attestations and verify them before deployment.
Secure Delivery and Runtime
Apply policy at the registry and deployment boundary. Restrict unsigned or unknown images, privileged execution, mutable tags, and unapproved sources. Keep base images minimal and patchable.
Runtime controls and observability still matter: a trusted build can contain a vulnerable dependency or behave dangerously after compromise.
Make the SBOM Operational
Store SBOMs in a searchable inventory. When a new vulnerability appears, ask which products, customers, environments, and versions are affected. Link findings to owners, remediation decisions, exceptions, and evidence.
Test the process with a tabletop dependency incident. Measure artifact coverage, provenance verification, time to identify exposure, remediation time, and expired exceptions.
DualByte's cybersecurity service can harden repositories, CI/CD, dependencies, and artifact controls as one supply-chain programme.
Sources
Need help with implementation?
Get a free consultation with the DualByte team for your business technology needs.