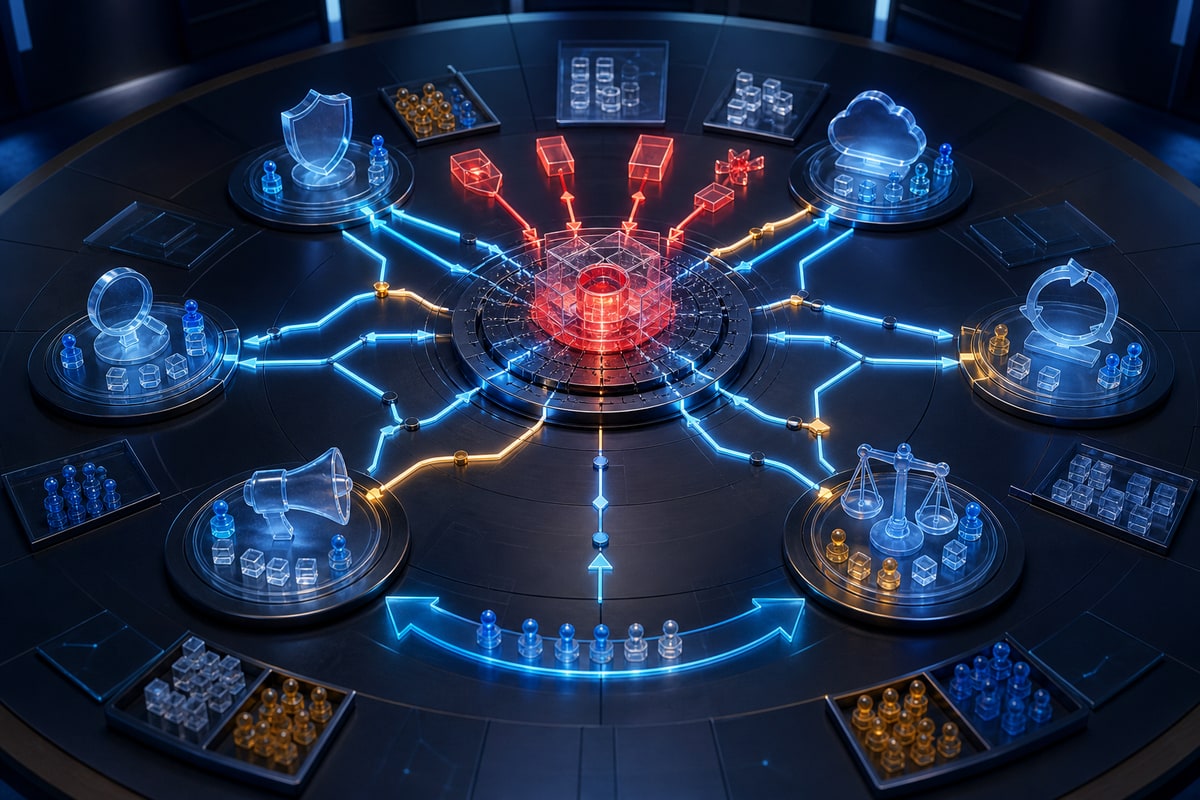
A data breach tabletop is a facilitated decision exercise, not a penetration test. It lets technical, legal, privacy, operations, communications, and leadership teams practise an evolving incident before real customers, deadlines, and uncertainty raise the stakes.
Set Learning Objectives
Choose three to five questions: Can the team establish command? Determine affected data? Stop exfiltration? Engage vendors? Make notification decisions? Continue critical operations?
Define participants, observers, facilitator, recorder, rules, duration, confidentiality, and success evidence. Senior decision-makers should participate rather than receive only a summary.
Build a Credible Scenario
Use your architecture, vendors, data, and business calendar. A scenario may begin with unusual cloud downloads, a stolen support account, ransomware, a malicious insider, or a vendor notification.
Prepare timed injects: incomplete alerts, customer questions, press contact, threat-actor claims, system outage, new forensic evidence, and a regulatory deadline. Do not reveal the whole story initially.
Exercise Decisions, Not Trivia
Ask who has authority to isolate systems, disable accounts, retain specialists, spend emergency funds, notify insurers, communicate publicly, and accept continuity risk.
Require participants to state what evidence they need, where they obtain it, who owns the action, and when they escalate. Capture assumptions and disagreements.
Cover the Full Response
Work through detection, triage, containment, evidence preservation, eradication, recovery, affected-data analysis, vendor coordination, legal assessment, notification, customer support, and follow-up.
Test alternate communications if normal identity or chat platforms are compromised. Consider employee welfare and handover during a long incident.
Handle Legal Duties Carefully
Bring qualified counsel to interpret applicable duties, privilege, notification thresholds, recipients, and timing. Indonesia's PDP Law includes controller duties concerning failure to protect personal data; exact action depends on facts and current applicable rules.
The exercise should test the decision process, not embed a generic legal conclusion in a technical playbook.
Observe and Improve
Evaluators should note decisions, delays, missing data, unclear roles, inaccessible contacts, unsafe workarounds, and effective practices. End with a hot wash while observations are fresh.
Publish an after-action report with prioritised actions, owners, dates, and validation. Update plans and runbooks, fund remediation, and re-exercise material gaps. Track closure and decision time—not how smoothly participants performed a rehearsed script.
DualByte's cybersecurity service can design and facilitate a scenario grounded in your technology and business risks.
Sources
Need help with implementation?
Get a free consultation with the DualByte team for your business technology needs.