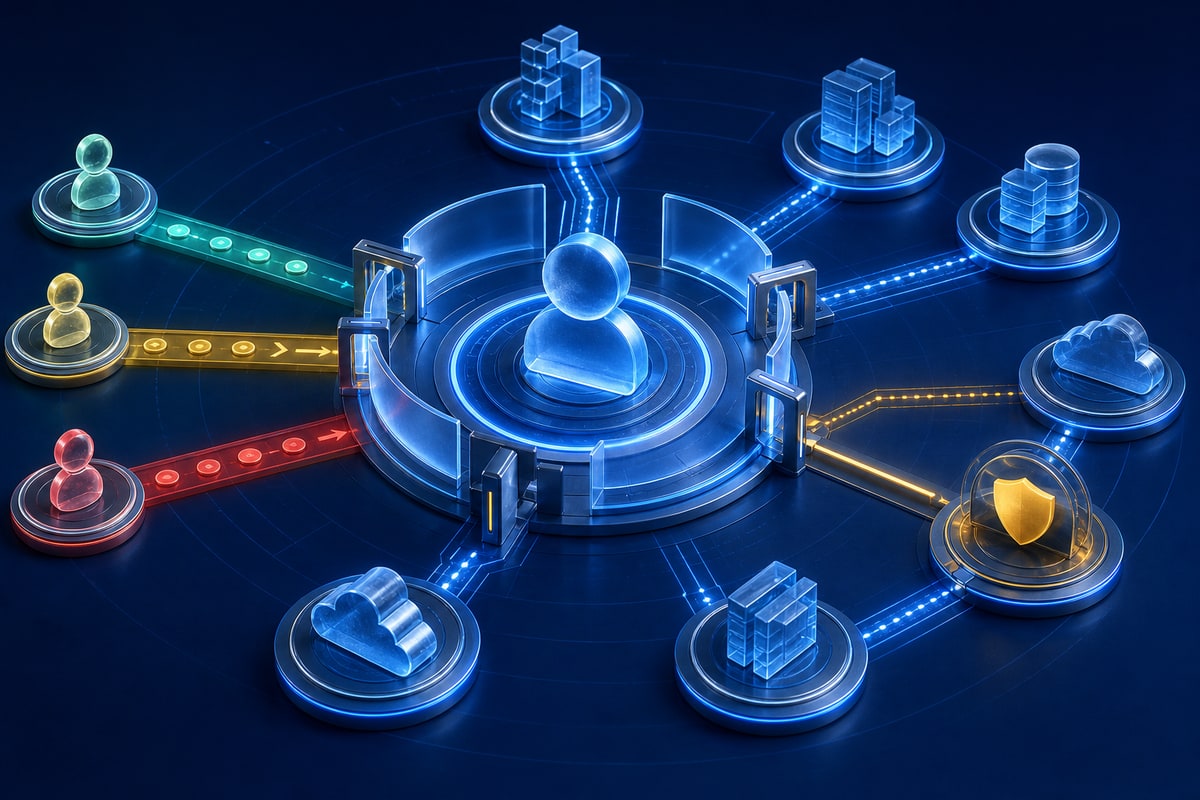
Identity and access management (IAM) should ensure that the right person or workload receives the right access for the right period—and that the company can prove it. Growing businesses need this discipline before application sprawl and role changes make manual access impossible to control.
Establish One Authoritative Identity
Choose the workforce directory and HR source that initiate joiner, mover, and leaver events. Give each person a unique account; prohibit shared administrator identities. Federate business applications through single sign-on where possible so policies and termination can be managed centrally.
Workload identities need the same attention. Services, automation, and CI/CD pipelines should use distinct, non-human identities rather than credentials borrowed from employees.
Require Strong Authentication
Prioritise phishing-resistant multi-factor authentication for administrators, finance, source control, cloud consoles, and remote access. Passkeys and hardware-backed security keys provide stronger resistance than reusable passwords or one-time codes.
Use conditional access thoughtfully. Device posture, location, risk, and resource sensitivity can trigger additional controls, but emergency access must remain possible and tested.
Design Roles Around Work
Begin with job functions and business tasks, not every historical permission. Separate standard access, elevated administration, and emergency access. Apply least privilege, but avoid hundreds of brittle roles that nobody understands.
For sensitive operations, use just-in-time elevation with approval, expiry, and audit. Separate incompatible duties—for example, creating a supplier and approving its payment.
Automate the Identity Lifecycle
Create baseline access from an approved role. Change access when a person moves teams, and revoke sessions, tokens, groups, devices, and application accounts promptly when they leave.
Include contractors and temporary staff with sponsors and expiry dates. Periodically reconcile the directory, HR roster, privileged systems, and SaaS applications to find orphaned accounts.
Review Access with Context
Managers cannot approve a list of cryptic group names responsibly. Reviews should show the resource, privilege, business purpose, last use, risk, and requested action. Review high-risk and privileged access more frequently.
Track decisions and completion, not just reviewer clicks. Repeated exceptions indicate that role design or application ownership needs improvement.
Log and Respond
Centralise authentication, privilege elevation, role changes, failed access, and administrative activity. Alert on impossible travel, unusual privilege, dormant-account use, MFA changes, and emergency-account activation.
Protect audit logs from alteration and define who investigates. IAM without response ownership becomes a passive archive.
A Phased Roadmap
First centralise identity, MFA, and leaver controls. Next integrate priority applications, establish roles, and inventory privileged access. Then automate lifecycle events, just-in-time elevation, reviews, and detection.
Measure SSO coverage, MFA coverage, leaver revocation time, orphaned accounts, standing privilege, review completion, and access-related incidents.
DualByte's cybersecurity service can assess identity risk and implement an IAM roadmap aligned with your systems and team.
Sources
Need help with implementation?
Get a free consultation with the DualByte team for your business technology needs.